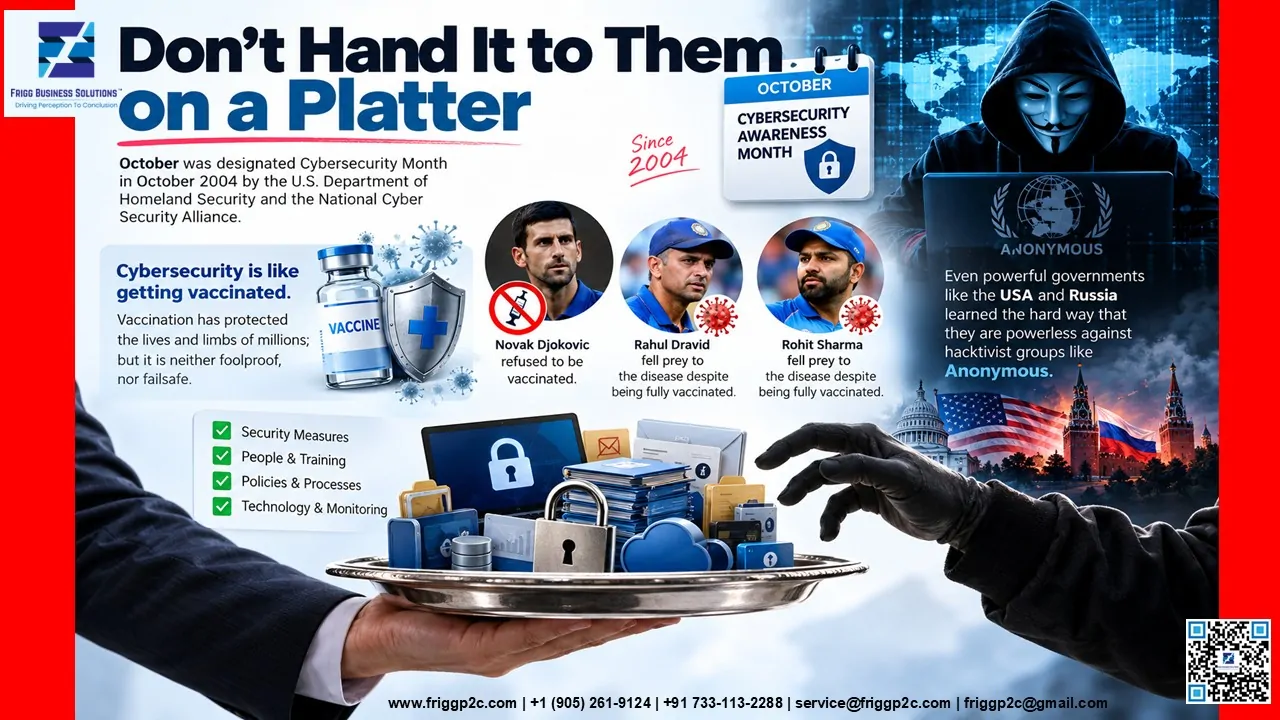
October was designated Cybersecurity Month in October 2004 by the U.S. Department of Homeland Security and the National Cyber Security Alliance. However, as the last 24 years have demonstrated, ensuring cybersecurity is like getting vaccinated. Vaccination has protected the lives and limbs of millions; but it is neither foolproof, nor failsafe. Remember the coronavirus pandemic? Different vaccines were developed around the world. A global sporting icon like Novak Djokovic refused to be vaccinated, while cricket icons like Rahul Dravid and Rohit Sharma fell prey to the disease despite being fully vaccinated. You can take as many cybersecurity measures as you like. In the end even powerful governments like the USA and Russia learned the hard way that they are powerless against hacktivist groups like Anonymous. Does it mean that you do away with cybersecurity measures? No. That would be throwing the baby out with the bathwater.
Human Error Is at the Root of Numerous Cybersecurity Disasters
How many times have you been told that human error was at the root of most data security breaches? From failure to train personnel on appropriate data security hygiene, updating security patches, and installing strong safeguards against breaches at security endpoints to people opening attachments of emails without first running it through a security scan first, or clicking on suspicious embedded links without verifying ― everything points back to human error. Several years ago Verizon had found in a survey that as many as 93 percent of malware attacks emanated from emails.
Be Aware of the Major Cybersecurity Threats
While hacktivism is a relatively new threat, the other major threats have been around for decades. Human carelessness, ignorance of actions’ consequences, bad actors spurred by greed, software with zero day vulnerabilities, faulty configurations, even downloading or updating apps or online tools without verifying their security lie at the core of most cybersecurity threats. Is there anything you can do to safeguard your organization and bottom line? Definitely. Cybersecurity Month is observed for precisely that reason ― to make people aware of the risks and how to circumvent them.
AI Tools Make Your Work Easier ― Think Again
These days, using AI tools to speed up work, or to simplify repetitive and boring tasks hides a major cybersecurity minefield. Since AI agent identities are rarely, if ever, fully disclosed to the user; it is vital to keep access to data at the least privileged level. It is possible to reduce and even eliminate the lethal trifecta ― the security vulnerability in artificial intelligence apps and tools built on large language models (LLMs) which can simultaneously access data, read external content, and take actions to accomplish tasks. One way to isolate and reduce risk would be to assess the existing architecture of the website to delimit the AI agents’ access to data, and its ability to send data out by focusing on the task it needs to accomplish. CSA explains how it works thus: “… a malicious attachment, a poisoned web page, a crafted subject line in an email the agent processes — can instruct the agent to use its privileged access and action capabilities in ways the user never intended”[i]. This indirect prompt injection becomes the attack vector.
The Threat Which Puts Individuals’ and Organizational Data in Jeopardy
When people search for AI tools, it is all too easy to fall prey to fake installers and malicious shared chatbots through ClickFix attacks. Its advanced cloaking techniques make it possible for it to bypass traditional fixes. Their interceptions occur through search engines via compromised websites, malvertising, and SEO poisoning. Ironically, many of these attacks came via impersonations of Claude, ChatGPT, and Codex.
Existing Vulnerabilities in Older Software
Many platforms like WordPress rely on PHP for their coding. However, in August 2026, Ryan Austin (a researcher at the California-based AI red-teaming firm Calif) and the cloud security company Wiz working independently discovered critical PHP security vulnerabilities — designated CVE-2026-109618 and CVE-2026-109619, known as PHP2Shell. Patching PHP installations urgently is recommended. Those who use Linux as their OS need to be aware of its inherent flaw called fragnesia.
Takeaway
Despite your best efforts, never assume that your cybersecurity systems are 100 percent secure. Eternal vigilance is the price you pay for data security and a healthy bottom line as major data breaches can cause huge monetary losses.
Protect your business from cubersecurity risks.
Connect with Frigg’s experts today for tailored guidance, proactive strategies, and compliant frameworks that strengthen security, ensure resilience, and accelerate confident growth outcomes.
Get in touch with us at: service@friggp2c.com, info@friggenix.ae, amit.sarkar@friggp2c.com, or Call us at: +971 58 137 9867 | +1 (905) 261-9124 | +1 (905) 261-9123 | +1 (866) 907-7227 | +91 733-113-2288
[i] https://labs.cloudsecurityalliance.org/research/csa-research-note-ai-agent-lethal-trifecta-capability-securi/